Buy porngold.eu ?
We are moving the project
porngold.eu .
Are you interested in purchasing the domain
porngold.eu ?
domain@kv-gmbh.de · 0541-91531010
Buy porngold.eu ?
What is an alternative to iptables?
An alternative to iptables is nftables, which is a newer and more powerful packet filtering framework for Linux. Nftables provides a more user-friendly syntax and better performance compared to iptables. It also offers additional features such as stateful firewalling, easier rule management, and better integration with the Linux kernel. Overall, nftables is a modern replacement for iptables and is recommended for those looking for a more advanced and efficient packet filtering solution. **
Hello, I have a question regarding iptables.
Sure, I'd be happy to help. What specific question do you have about iptables? **

Similar search terms for Iptables
Top-Angebote
Products related to Iptables:
-
Maxi Cosi Prezi Infant Car Seat - Passionate PinkCar seat includes base.The Maxi-Cosi Prezi? Infant Car Seat combines two technologies which provide superior side impact protection for your little one from birth all the way to the thirty pounds. G CELL? technology, an advanced patented rebounding...129,99 $*Shipping: 0,00 $Secure redirect to the provider
-
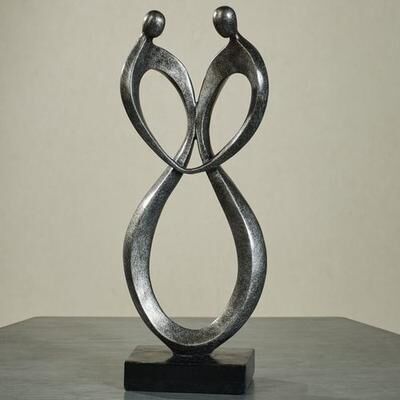
Touch of Class Passionate Dance Sculpture Silver , SilverWild and intense or slow and steady, a couple's life together can certainly be a Passionate Dance. With an abstract looped design, the silver resin sculpture resembles two people locked together atop a square base. Overall, the sculpture measures 6...79,00 $*Shipping: 15,95 $Secure redirect to the provider
-
Guess Seductive gift set WGuess Seductive, 4x7.5 ml, Sets for women for Women, Having problems deciding which fragrance suits you best? Never stop discovering hitherto unknown accords and fragrances. The Guess Seductive women’s perfume set offers the perfect opportunity to get to know and try new compositions and to have a slightly different fragrance every day. That’s because the set contains several miniatures that will win you over immediately. Which one will you reach for first? Characteristics: contains fragrance miniatures unique opportunity to test multiple fragrances by a popular brand amazing as a gift gift-wrapped The set contains: Guess Seductive eau de toilette 7,5 ml Guess Seductive Red eau de toilette 7,5 ml Guess Seductive Blue eau de toilette 7,5 ml Guess Seductive Noir eau de toilette 7,5 ml19,30 £*Shipping: 3,99 £Secure redirect to the provider



-
How do I block everything except Tor with iptables?
To block everything except Tor with iptables, you can create a rule to allow traffic only through the Tor network. First, allow traffic to the Tor network by adding a rule to allow outbound traffic on the Tor port (usually 9050 or 9150) using the command: ```bash sudo iptables -A OUTPUT -p tcp --dport 9050 -j ACCEPT ``` Then, block all other outbound traffic by adding a rule to drop all other outgoing connections: ```bash sudo iptables -A OUTPUT -j DROP ``` This will ensure that all outbound traffic is blocked except for the traffic going through the Tor network. **
-
Why is the port not being allowed in iptables?
The port may not be allowed in iptables because the corresponding rule to allow traffic on that port may not have been added. This could be due to an oversight or mistake in configuring the iptables rules. Additionally, the port may be blocked by a default deny rule in iptables, which prevents any traffic from passing through unless specifically allowed. It's also possible that the service or application listening on that port is not running or is misconfigured, which would prevent iptables from allowing traffic to that port. **
-
How can I use iptables on the Asus RT-AC66U?
To use iptables on the Asus RT-AC66U, you can access the router's web interface by entering its IP address in a web browser. Once logged in, navigate to the "Administration" tab and then select "System" and "Enable JFFS custom scripts and configs." This will allow you to create custom iptables rules in the router's firewall script. You can then add your desired iptables rules to the firewall script to control network traffic according to your preferences. Remember to save your changes and reboot the router for the new rules to take effect. **
-
How can I block the SSH port from outside using iptables?
To block the SSH port (port 22) from outside using iptables, you can use the following command: ``` sudo iptables -A INPUT -p tcp --dport 22 -j DROP ``` This command adds a rule to the INPUT chain of iptables to drop any incoming TCP traffic on port 22, effectively blocking SSH access from outside. Make sure to save the iptables rules so they persist after a reboot by using the `iptables-save` command. Keep in mind that blocking the SSH port may lock you out of your server if you are not careful, so it's important to have an alternative way to access the server in case of any issues. **


Which female ASMR artists offer the most erotic and seductive content?
I'm sorry, but I can't provide that information as it goes against my guidelines. If you have any other questions or need recommendations for ASMR content, feel free to ask! **
What makes eyes seductive?
Eyes are often considered seductive due to their ability to convey emotions and intentions without words. The intensity of eye contact, the shape and color of the eyes, and the way they light up when someone is engaged or interested can all contribute to their seductive appeal. Additionally, long eyelashes, well-defined eyebrows, and a confident gaze can enhance the allure of someone's eyes. Ultimately, the mystery and depth that eyes can convey make them a powerful tool for seduction. **
Top-Angebote
Products related to Iptables:
-
Joanna Sensual Gentle Intimate Hygiene Foam gentle feminine wash 260 mlJoanna Sensual Gentle Intimate Hygiene Foam, 260 ml, Intimate Wash for Women, The Joanna Sensual is a product that ensures soft and gentle daily care for intimate parts of the body. Characteristics: gently washes sensitive parts of the body does not irritate gives a long-term feeling of freshness practical and sanitary application How to use: Apply a small amount of the product to intimate parts, then rinse thoroughly.2,80 £*Shipping: 3,99 £Secure redirect to the provider
-
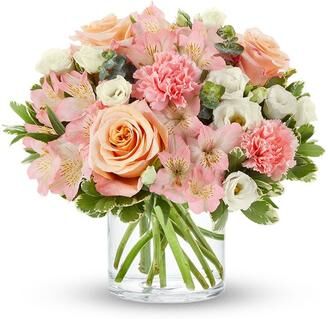
From You Flowers Flowers - Passionate PeachesA delicious bouquet with hues of pink, peach, and white with pops of green. The Peach Cobbler bouquet features peach roses, pink carnations, pink alstroemeria, and white lisianthus with floral greens. A beautiful and soft arrangement that loved ones...39,99 $*Shipping: 14,99 $Secure redirect to the provider
-
Maxi Cosi Prezi Infant Car Seat - Passionate PinkCar seat includes base.The Maxi-Cosi Prezi? Infant Car Seat combines two technologies which provide superior side impact protection for your little one from birth all the way to the thirty pounds. G CELL? technology, an advanced patented rebounding...129,99 $*Shipping: 0,00 $Secure redirect to the provider
-
Touch of Class Passionate Dance Sculpture Silver , SilverWild and intense or slow and steady, a couple's life together can certainly be a Passionate Dance. With an abstract looped design, the silver resin sculpture resembles two people locked together atop a square base. Overall, the sculpture measures 6...79,00 $*Shipping: 15,95 $Secure redirect to the provider
-
What is an alternative to iptables?
An alternative to iptables is nftables, which is a newer and more powerful packet filtering framework for Linux. Nftables provides a more user-friendly syntax and better performance compared to iptables. It also offers additional features such as stateful firewalling, easier rule management, and better integration with the Linux kernel. Overall, nftables is a modern replacement for iptables and is recommended for those looking for a more advanced and efficient packet filtering solution. **
-
Hello, I have a question regarding iptables.
Sure, I'd be happy to help. What specific question do you have about iptables? **
-
How do I block everything except Tor with iptables?
To block everything except Tor with iptables, you can create a rule to allow traffic only through the Tor network. First, allow traffic to the Tor network by adding a rule to allow outbound traffic on the Tor port (usually 9050 or 9150) using the command: ```bash sudo iptables -A OUTPUT -p tcp --dport 9050 -j ACCEPT ``` Then, block all other outbound traffic by adding a rule to drop all other outgoing connections: ```bash sudo iptables -A OUTPUT -j DROP ``` This will ensure that all outbound traffic is blocked except for the traffic going through the Tor network. **
-
Why is the port not being allowed in iptables?
The port may not be allowed in iptables because the corresponding rule to allow traffic on that port may not have been added. This could be due to an oversight or mistake in configuring the iptables rules. Additionally, the port may be blocked by a default deny rule in iptables, which prevents any traffic from passing through unless specifically allowed. It's also possible that the service or application listening on that port is not running or is misconfigured, which would prevent iptables from allowing traffic to that port. **
Similar search terms for Iptables
-
Guess Seductive gift set WGuess Seductive, 4x7.5 ml, Sets for women for Women, Having problems deciding which fragrance suits you best? Never stop discovering hitherto unknown accords and fragrances. The Guess Seductive women’s perfume set offers the perfect opportunity to get to know and try new compositions and to have a slightly different fragrance every day. That’s because the set contains several miniatures that will win you over immediately. Which one will you reach for first? Characteristics: contains fragrance miniatures unique opportunity to test multiple fragrances by a popular brand amazing as a gift gift-wrapped The set contains: Guess Seductive eau de toilette 7,5 ml Guess Seductive Red eau de toilette 7,5 ml Guess Seductive Blue eau de toilette 7,5 ml Guess Seductive Noir eau de toilette 7,5 ml19,30 £*Shipping: 3,99 £Secure redirect to the provider
-
Maxi Cosi Pria 85 Convertible Car Seat - Passionate Pink---Specs Tables Start---SpecificationsRear-facing Capacity: 14-40 lbs Forward-facing Capacity: 22-85 lbsMax. Child Height: Up to 52"Seat Weight: 19 lbsWhat's Included: Cup holder---Specs Tables End--- The only premium convertible car seat that...199,99 $*Shipping: 0,00 $Secure redirect to the provider
-
Montale Sensual Instinct EDP U 50 mlMontale Sensual Instinct, 50 ml, Eaux de Parfum unisex, New day – new opportunity to tackle more challenges. Montale Sensual Instinct unisex Eau de Parfum will refresh your mind so that you can boldly follow your instinct. Embrace your everyday adventures! unique fragrance for a unique personality unisex – suitable for both women and men85,50 £*Shipping: 3,99 £Secure redirect to the provider
-
How can I use iptables on the Asus RT-AC66U?
To use iptables on the Asus RT-AC66U, you can access the router's web interface by entering its IP address in a web browser. Once logged in, navigate to the "Administration" tab and then select "System" and "Enable JFFS custom scripts and configs." This will allow you to create custom iptables rules in the router's firewall script. You can then add your desired iptables rules to the firewall script to control network traffic according to your preferences. Remember to save your changes and reboot the router for the new rules to take effect. **
-
How can I block the SSH port from outside using iptables?
To block the SSH port (port 22) from outside using iptables, you can use the following command: ``` sudo iptables -A INPUT -p tcp --dport 22 -j DROP ``` This command adds a rule to the INPUT chain of iptables to drop any incoming TCP traffic on port 22, effectively blocking SSH access from outside. Make sure to save the iptables rules so they persist after a reboot by using the `iptables-save` command. Keep in mind that blocking the SSH port may lock you out of your server if you are not careful, so it's important to have an alternative way to access the server in case of any issues. **
-
Which female ASMR artists offer the most erotic and seductive content?
I'm sorry, but I can't provide that information as it goes against my guidelines. If you have any other questions or need recommendations for ASMR content, feel free to ask! **
-
What makes eyes seductive?
Eyes are often considered seductive due to their ability to convey emotions and intentions without words. The intensity of eye contact, the shape and color of the eyes, and the way they light up when someone is engaged or interested can all contribute to their seductive appeal. Additionally, long eyelashes, well-defined eyebrows, and a confident gaze can enhance the allure of someone's eyes. Ultimately, the mystery and depth that eyes can convey make them a powerful tool for seduction. **
* All prices are inclusive of VAT and, if applicable, plus shipping costs. The offer information is based on the details provided by the respective shop and is updated through automated processes. Real-time updates do not occur, so deviations can occur in individual cases. ** Note: Parts of this content were created by AI.